A stock theme is not a shortcut at scale; it’s a ceiling. The fastest path to a secure, brand-consistent, and compliant enterprise site in 2026 is a lean custom theme tied to your design system and governance model. This guide shows you how to run custom wordpress theme development the right way, with concrete steps and tools you can put to work this week.
As your portfolio grows, so do the risks: slow pages hurt conversions, one-off brand fixes multiply, and plugin stacks turn into attack surfaces. Moreover, legal and regional rules add real load on your process. Therefore, you need code, content models, and release workflows that match enterprise demands, not hobby sites.
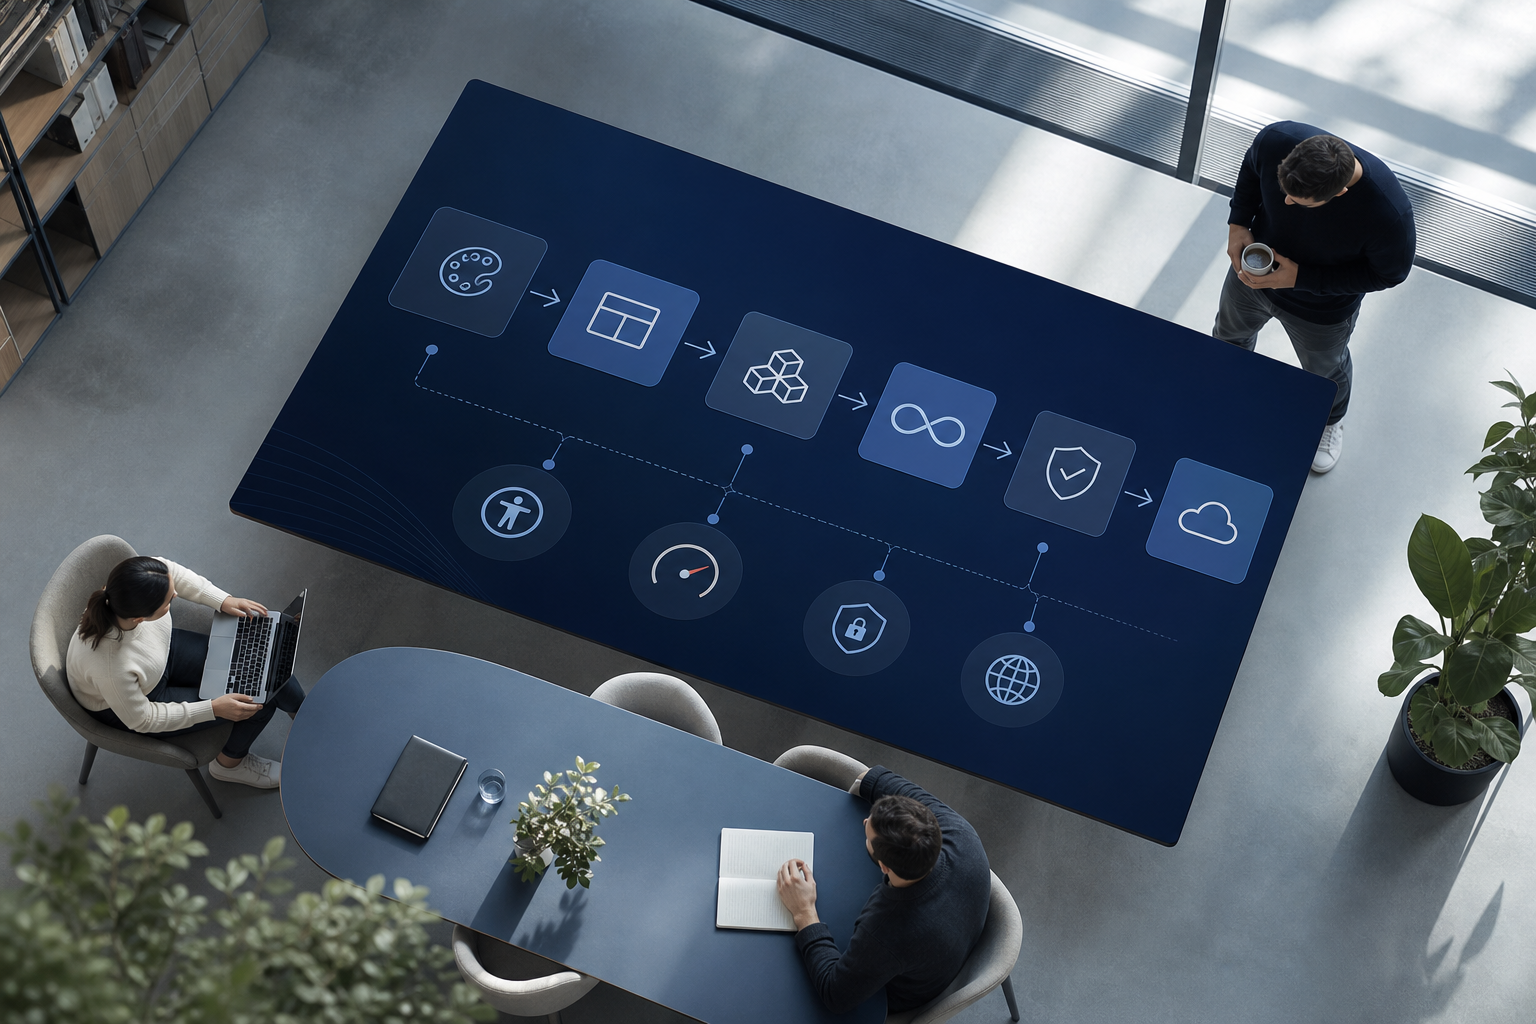
Here’s the answer in one line: build a component-based theme around your design tokens, use theme.json and the block editor for layout control, test to WCAG 2.2 AA, hit Core Web Vitals, and deploy with CI/CD to a hardened host. Then you can scale content, brands, and markets with confidence.
 , CI/CD (GitHub Actions), hosting (WP Engine/Pantheon), and monitoring (Core Web Vitals). Corporate style, blue/gray palette, vector icons, high-resolution)
Why Enterprise Companies Outgrow Off-the-Shelf WordPress Themes
Performance and Brand
Off-the-shelf themes carry features you do not need. As a result, they ship extra JavaScript, CSS, and database queries that slow the site. At enterprise traffic levels, that bloat compounds. Per Google’s guidance, “good” Core Web Vitals targets are LCP ≤ 2.5 s, CLS ≤ 0.1, and INP ≤ 200 ms (Core Web Vitals guidance). Hitting those targets on a generic theme is hard because you can’t fully control render paths and asset loading.
Brand drift is the next tax. Your brand team ships a new token set, but the theme locks typography scales and spacing. Consequently, your teams patch styles per page or per market. Six months later, you have 14 button styles and no single source of truth. A custom theme maps tokens to block styles, patterns, and templates, so design and content stay in sync.
Security, Compliance, and Governance
Security and compliance pressure grow with scale. You may need strict roles, audit logs, SSO, and a content security policy. Furthermore, you likely need to meet WCAG 2.2 AA (WCAG 2.2 overview) and handle GDPR lawful bases (GDPR text, 2016/679). Stock themes don’t solve this. A custom stack lets you enforce safe defaults: server-side render for key blocks, limited iframes, and no third-party scripts by default.
Finally, governance breaks with multisite and multi-brand. For example, marketing may need patterns locked for regulated regions, while product marketing needs flexible landing pages. Therefore, you need theme-level controls and roles that support both. This is exactly where custom wordpress theme development pays for itself across many launches.
Where Stock Themes Break at Scale
- Performance: shared features add unused CSS/JS you can’t remove.
- Brand: one-off overrides fragment your design language fast.
- Security: bundled code widens your attack surface and review scope.
- Governance: no granular control for roles, blocks, or markets.
"Their developer quickly resolved an urgent issue and improved performance. Their responsiveness and technical skills saved the day." — David R.
7-Step Framework for Enterprise Custom WordPress Theme Development
You don’t need a big-bang rebuild. Instead, follow a staged framework that gives results early and keeps risks low. This is the same path I use to align marketing, design, security, and engineering. It also maps well to Theme & Plugin Solutions and to CMMI and ISO certified processes for predictable delivery.
This framework guides your custom wordpress theme development from audit to handoff. Each step outputs artifacts your team can own and reuse.
The Steps
- Requirements audit
- Gather KPIs, risk constraints, and canonical user flows. Define non-negotiables: Vitals budgets, WCAG 2.2 AA, SSO, roles, regions.
- Design system creation
- Build tokens in Figma (colors, type, spacing). Export to JSON. Define core blocks and patterns mapped to real content.
Plan and Align
- Architecture planning
- Choose SSR for dynamic blocks. Set cache layers. Plan data models (CPTs, taxonomies). Define feature flags and environments.
- Starter theme selection
- Pick a lean starter (e.g., block-first) with no page-builder lock-in. Confirm PHP 8.x and WordPress 6.x support.
Build and Validate
- Component-based build
- Use theme.json for styles, block supports, and presets. Register patterns/variations. Ship only required assets, split per template.
- QA & accessibility
- Test keyboard paths, color contrast, focus order. Validate against WCAG 2.2 AA. Run performance budgets on PRs.
- Deployment & handoff
- Set GitHub Actions for CI/CD. Enforce code review. Document patterns, roles, and runbooks for releases and rollbacks.
Specifically, your theme should set strict default styles in theme.json, not hardcoded CSS. Therefore, editors get guardrails in the block editor without custom code per page. For performance, load CSS per-template and defer non-critical JS. For audits, add PR checks that fail when LCP or INP regress beyond your budget. Per Google’s targets, LCP should be 2.5 seconds or less, and INP should be 200 milliseconds or less (source above).
Moreover, bake accessibility into each component. For example, ensure Heading blocks follow a logical order, and navigation uses proper aria attributes. Then back this with automated checks and manual screen-reader passes. Finally, codify deployment: GitHub Actions for tests and builds; promotion from staging to prod with approvals; and rollbacks in one click.
**Get dedicated WP devs today →
Also Read!
Small Business Guide to WordPress Maintenance and Support
Best WordPress Maintenance and Support for Small Businesses in 2026
5 Mistakes Enterprise Teams Make With Custom WordPress Themes
Teams don’t fail on code first; they fail on planning and guardrails. As a result, costs rise in year two, not month one. Here are the traps I see in audits and how to avoid them.
Skipping a design system turns every page into a new design. Without tokens, teams ship ad-hoc CSS and drift from the brand in weeks. Instead, define tokens once and bind them to blocks, patterns, and templates.
Ignoring the block editor and hardcoding layouts makes your theme brittle. Editors end up filing tickets for small changes. Therefore, use theme.json, block supports, and patterns to let marketing ship pages without code while you keep control.
Costly WordPress Theme Errors
- Skipping a design system: no tokens, endless overrides, weak reuse.
- Ignoring block editor: custom PHP templates for every layout.
- Hardcoding styles vs. theme.json: no editorial guardrails.
- Neglecting multisite: no shared patterns, no per-site overrides.
- No maintenance plan: no patch cadence, rising security debt.
Security and compliance need steady care. Without a plan, you will miss plugin updates, theme patches, or policy changes. Furthermore, legal and IT will ask for logs, SSO, and export controls with little notice. Set a quarterly review for changes in WCAG, privacy, and browser security. If you handle personal data, align retention and consent to GDPR principles like lawfulness, fairness, and transparency (see the GDPR source above).
From a cost view, a plan beats ad-hoc fixes. Ongoing support and maintenance keep your stack lean and safe. In the long run, you pay less by reducing rework and outages. This is long-term cost efficiency in practice, not theory.
"They delivered ahead of schedule and were easy to work with. The custom theme matched our vision." — John M.
Tools and Partners for Enterprise WordPress Theme Projects
The right stack cuts risk and time-to-value. For design, keep a single source of truth. In addition, wire CI/CD and testing into each pull request. For hosting, choose platforms that support cache layers, staging, and security controls.
- Design system: Figma for tokens, components, and handoff. Export tokens to JSON for your theme.json.
- CI/CD: GitHub Actions for linting, unit tests, E2E tests, and performance budgets on each PR.
- Hosting: WP Engine or Pantheon for staging flows, backups, and edge cache. Ask for SSO and audit logging.
- Security: Require SSO, 2FA, WAF, and CSP. For policy alignment, map controls to ISO/IEC 27001 (ISO/IEC 27001 information security).
For partners, you have two routes. First, embed dedicated WordPress developers who know block themes, theme.json, and CI/CD. Second, engage a specialist agency for Theme & Plugin Solutions and backlog coverage. Agencies like Passion 8 Press offer Dedicated WordPress Developers, quick onboarding, an experienced in-house team, transparent communication, and daily updates. They can also take on Custom WordPress Plugin Development when you need integrations beyond the theme.
As you shortlist partners in 2026, ask for proof of CMMI and ISO certified processes and sample runbooks. Furthermore, request a one-sprint pilot: one component library, two patterns, and a staging deploy. You’ll learn more in two weeks than in a 40-slide RFP.
Key Takeaways and What to Do This Week
- Build for speed, brand, and governance first. A lean, component-based theme with theme.json and patterns beats feature-heavy stock code.
- Meet standards by design: Core Web Vitals (LCP ≤ 2.5 s, INP ≤ 200 ms, CLS ≤ 0.1), WCAG 2.2 AA, and GDPR principles.
- Treat multisite as a product, not a setting. Share patterns and tokens; allow safe per-site overrides.
- Plan upkeep: quarterly audits, CI on PRs, and a clear patch cadence. That’s how you get long-term cost efficiency.
- Use partners and tools to reduce risk: Figma tokens, GitHub Actions, and hardened hosting. Consider a sprint pilot to prove fit.
What to do this week:
- Day 1: Run a 90-minute requirements audit. Capture KPIs, Vitals budgets, roles, regions, WCAG level, and SSO needs. Decide must-have vs. nice-to-have.
- Day 2: Define or refine design tokens in Figma. Export to JSON. Draft three core blocks and two patterns for your most-used page.
- Day 3: Choose a lean starter theme. Set up a repo with GitHub Actions (lint, unit tests, Lighthouse CI). Add budgets for LCP/INP/CLS.
- Day 4: Wire theme.json with colors, type scale, spacing, and block supports. Register one template and two patterns mapped to real content.
- Day 5: Test keyboard paths and color contrast. Validate against WCAG 2.2 AA. Deploy to staging on WP Engine or Pantheon. Hold a 30-minute go/no-go review.
Custom wordpress theme development is a product, not a project. Start small, ship value each sprint, and codify your wins in tokens, patterns, and tests. You’ll feel the change in your next launch window.
**Start your roadmap in 5 days →
"The process was stress-free. The developer understood our vision and delivered a site that exceeded expectations." — Maria L.